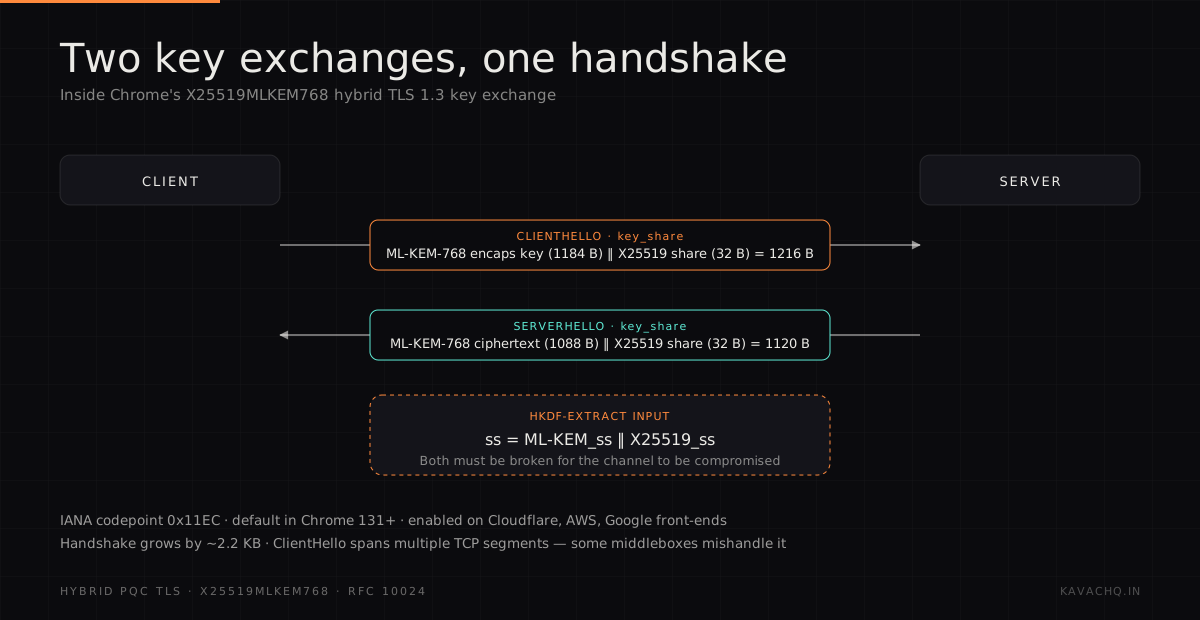
The IANA codepoint 0x11EC is the
most important number in any TLS handshake that uses it. It
identifies a named group called X25519MLKEM768:
the hybrid combination of classical X25519 elliptic-curve
Diffie-Hellman and the NIST ML-KEM-768 key encapsulation
mechanism, now specified in
RFC 10024.
Chrome made it the default from Chrome 131 (November 2024),
replacing the earlier pre-standard X25519Kyber768 group;
Cloudflare, AWS, and Google's front-ends shipped server support
over the same window.
For a CISO of an Indian bank, three questions matter. What is this thing? What does it cost on the wire? What has to be true at the bank's own edge so the channel actually completes?
What the hybrid construction does
In a TLS 1.3 handshake using a single (non-hybrid) named group, the client puts one key share in the ClientHello, the server responds with one key share in the ServerHello, both sides perform the key agreement, and the resulting shared secret feeds the TLS key schedule via HKDF.
In the hybrid construction, the client puts two shares in a single ClientHello key share — the ML-KEM-768 encapsulation key (1184 bytes) followed by an X25519 share (32 bytes), 1216 bytes concatenated. The server responds with two outputs in the ServerHello — the ML-KEM-768 ciphertext (1088 bytes) followed by its X25519 share (32 bytes), 1120 bytes in all. Both sides compute their respective shared secrets, concatenate them (ML-KEM secret ‖ X25519 secret), and feed the result into HKDF-Extract as if it were a single shared secret. From there the TLS key schedule is unchanged.
Note the order: ML-KEM comes first. RFC 10024 calls this out — the name X25519MLKEM768 does not follow the usual hybrid naming convention, and the concatenation order is reversed for historical reasons. The other two hybrid groups the RFC defines, SecP256r1MLKEM768 and SecP384r1MLKEM1024, put the ECDHE share first. If you are writing a parser or a test vector, get this right.
The mathematical property that earns the work: for an attacker to recover the channel keys, they must break both the X25519 key exchange and the ML-KEM key exchange. Breaking only one leaves the concatenated input unrecoverable. This is the same composition principle behind "defence in depth" applied at the cryptographic primitive level.
Why hybrid, not pure ML-KEM
It would be simpler to just switch from X25519 to ML-KEM. The reason that hasn't happened is concern about ML-KEM itself. Lattice-based cryptography is younger than elliptic-curve cryptography. The lattice security assumptions are well-studied and the parameter sets were chosen with generous margins, but cryptanalytic surprises happen — the history of cryptography is littered with schemes that looked solid for a decade before breaking. Hybrid lets the deployment community gain operational experience with ML-KEM while keeping the classical fallback until enough confidence accumulates.
If lattice schemes are ever broken, hybrid deployments degrade to classical-only security — which is the security level you had before you started. If they're not, you have post-quantum security and classical security simultaneously. The cost of being wrong is bounded; the cost of being right is small.
What changes on the wire
The handshake grows. ClientHello picks up an extra ~1.2 KB from the ML-KEM-768 encapsulation key; ServerHello picks up an extra ~1.1 KB from the ciphertext. Total round-trip handshake payload grows by ~2.2 KB. On modern paths this is a non-event — modern TCP initial windows accommodate it without extra round trips on most connections.
The two places it bites:
- Packet boundaries. The ClientHello now reliably exceeds the 1500-byte MTU, so it spans multiple TCP packets; a small number of middleboxes don't handle a split ClientHello correctly. Inspect-and-rewrite proxies are the usual culprit.
- Initial connection latency. If your end-user is on a constrained mobile network with high packet loss, the larger handshake means more opportunity for a retransmission. Measure rather than assume.
What to check at your edge
For an Indian bank running TLS termination on commercial hardware ADC, three things to verify:
- Vendor firmware supports the hybrid group. Several ADC vendors have added X25519MLKEM768 support; confirm the specific firmware train you run — feature parity across LTS branches lags the latest release.
- Cipher suite ordering and group preference. Configure the box to prefer the hybrid group when offered. Most ADCs default to the first acceptable group from the client; for browsers that put X25519MLKEM768 first, this gives PQC by default.
- Logging captures the negotiated group. Many ADC logs default to TLS version + cipher only. Add the named group to the log line — you cannot prove migration progress without it.
If your ADC is on a firmware line where hybrid support never shipped, that's a different conversation — the edge box has to be upgraded or replaced. Plan the upgrade now while there's still a vendor support window, not in the quarter you're reporting to the audit committee.