Product Built for the regulator you answer to

Find it. Fix it. Prove it.

Four products, one job each. KavachQ Discover finds the cryptography you run and what a quantum computer would break first. KavachQ Migrate fixes it with a phased plan and changes you approve. KavachQ Gateway puts post-quantum TLS in front of the applications you cannot change yet. KavachQ Seal proves it with CBOMs signed with a post-quantum signature (ML-DSA-65) that an auditor, a regulator or a tender committee can check offline. In depth for India's DST National Quantum Mission roadmap, RBI, SEBI, IRDAI and CERT-In; our region guides cover SAMA, NCSC, the EU roadmap, ASD and US federal dates.

🔒 The free scan reads only what's publicly negotiated in a TLS handshake — no sign-in, nothing stored.

KavachQ · Cryptographic inventory
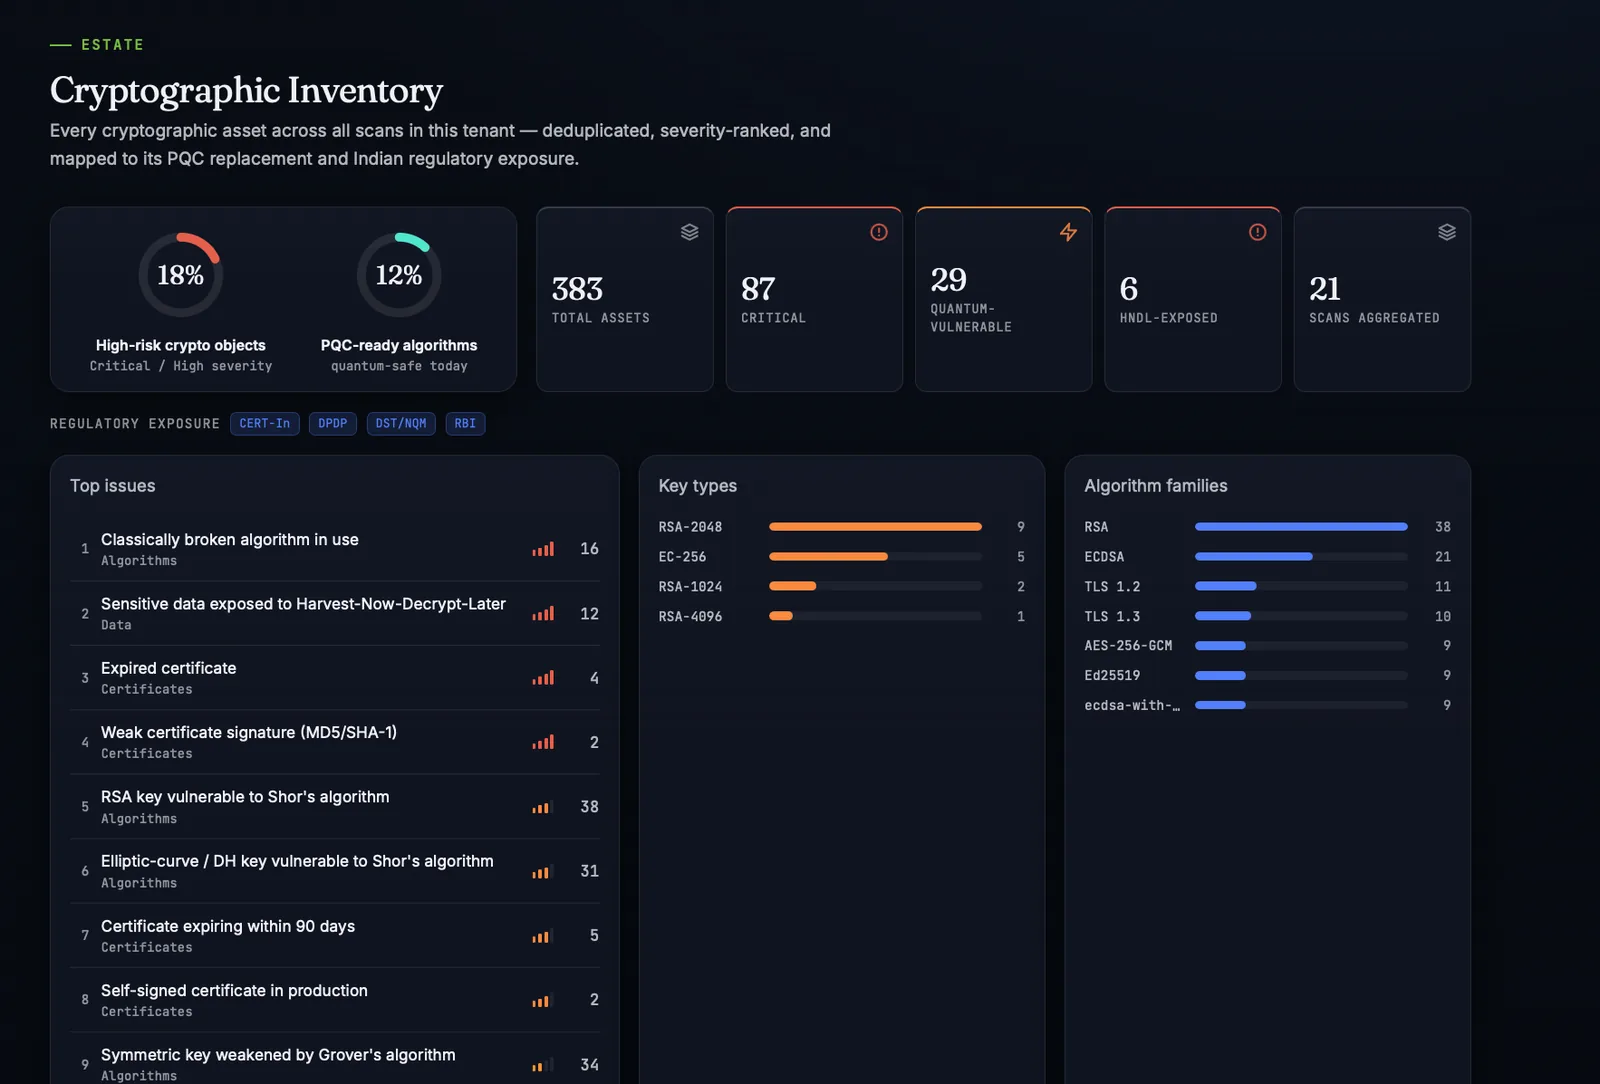
KavachQ console — cryptographic inventory dashboard: high-risk crypto objects, PQC-ready share, total assets, and algorithm families ranked by severity.
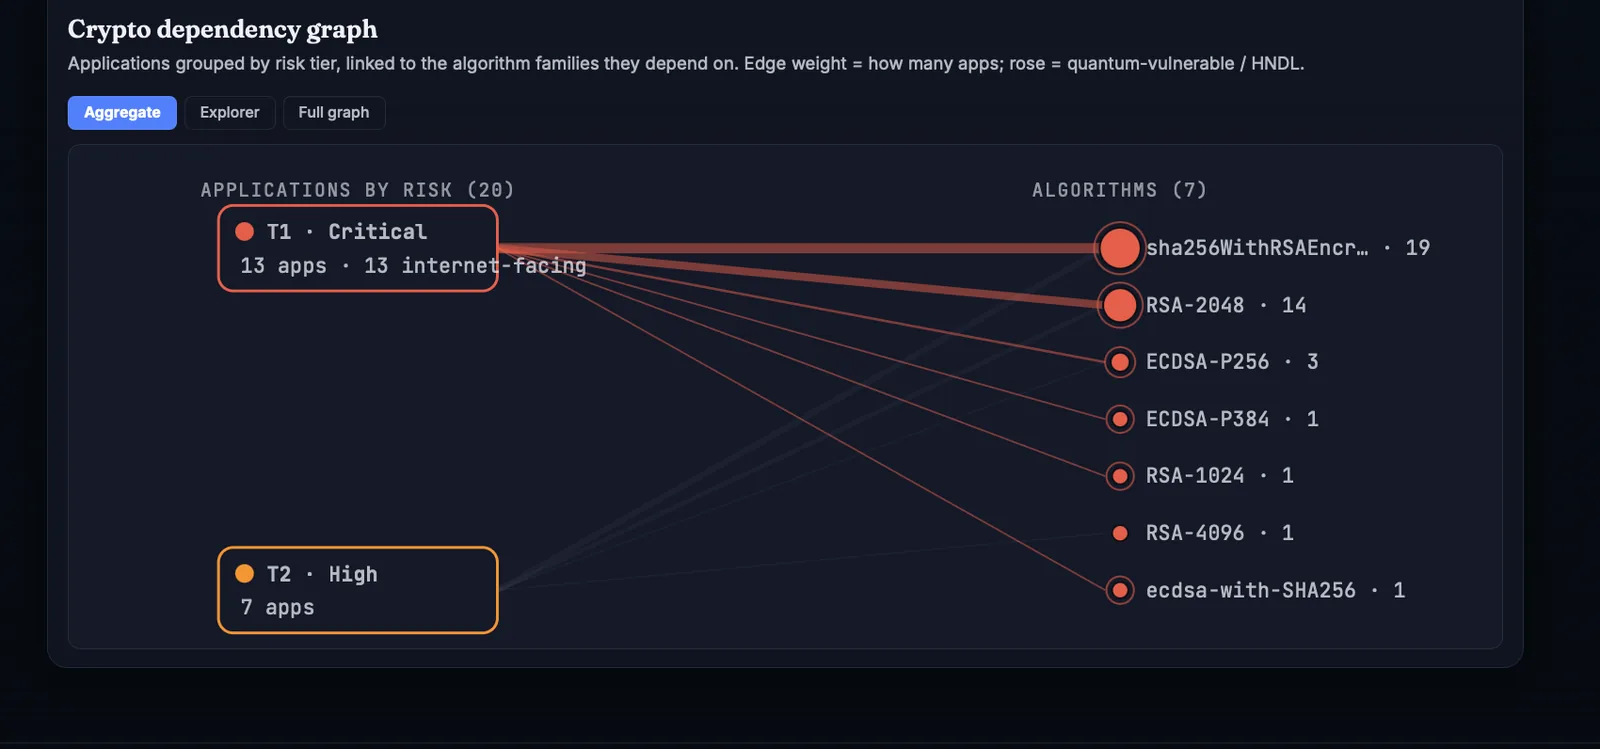
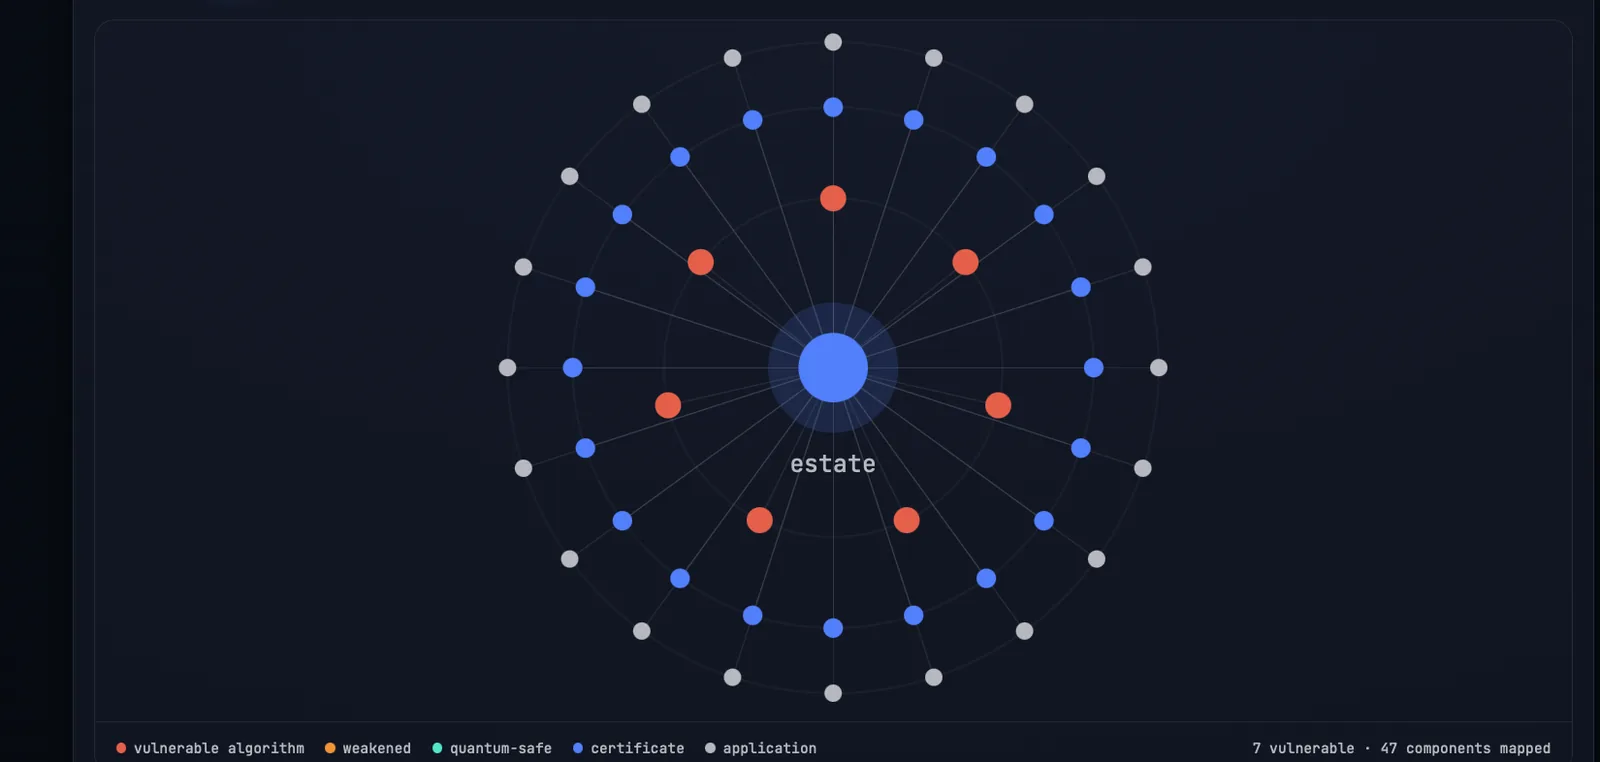
The working console — not a mockup. A real cryptographic-inventory view, captured on a demo tenant. Numbers are illustrative; real client estates never leave your environment. See more real screens ↓
Where KavachQ fits

Made for the regulator you answer to

KavachQ goes deep on India's framework and deadlines, runs inside your own boundary, and gives you evidence any auditor can check — wherever you are regulated.

Your regulator's timeline

In depth for India's DST/NQM (with its M1/M2/M3 milestones), RBI, SEBI and CERT-In; our region guides cover SAMA, NCSC, the EU roadmap, ASD and US federal dates.

Runs in your environment

In-VPC, on-prem, or air-gapped self-hosted Docker. Your cryptographic inventory stays inside your boundary.

Open, portable evidence

The inventory is a signed CBOM in open CycloneDX 1.7 — evidence your own auditors can reproduce, and that travels with you. No lock-in.

Try before you talk to us

Start with a free public scan of any domain's TLS — no sign-in, results in seconds. See the product work before a conversation.

The products

Four products. One job each.

Find what you have, fix it in the right order, and prove it to anyone who asks — with Kavach Copilot to ask the regulation or explain a finding.

Know every lock a quantum computer can open, and which to change first. Discover inventories the cryptography across your estate and ranks it by quantum risk.

Collect

49 of 51 shipped
  • Live TLS and SSH probes; external attack surface after a domain-ownership check
  • Passive capture, including OT protocols
  • In-network collector for internal estates
  • Code, config, keystores, certificates and Git organisations
  • Parses exports from cloud, Kubernetes, databases, HSM, mainframe, payments, VPN and mobile
  • Imports and merges other tools' CBOMs and SBOMs

Assess

52 of 52 shipped
  • Four-tier (T1–T4) quantum-risk rating per asset, DST-aligned; a 0–100 PQC-Ready score per scan
  • Harvest-now-decrypt-later exposure and Mosca timeline
  • Risk heat map and business view
  • Crypto-agility maturity (NIST CSWP 39)
  • CVE, KEV, EPSS, CWE and FIPS 140-3 status
  • Regulator gap report; 14 framework packs

Change it safely, and check that the change took. Migrate turns findings into a dated plan, then makes the change with a named approver and a tested way back.

Roadmap

19 of 19 shipped
  • Phased P0 / P1 / P2 plan with the algorithm choice for each asset
  • DST and NQM deadlines, harmonised with global ones
  • Budget model and vendor-blocked tasks
  • Push to Jira and ServiceNow, with two-way status sync from Jira

Change

20 of 21 shipped
  • Change packs for nginx, HAProxy, Apache and ACME
  • A named approver signs off before anything runs
  • Apply over SSH, with a tested rollback
  • Re-checks the endpoint to confirm the change took effect
  • Works with KavachQ Gateway for apps you cannot change

Scope today: Migrate changes TLS terminators (nginx, HAProxy, Apache, ACME). It does not rewrite application code or touch OT.

KavachQ Seal

Prove it.

Proof anyone can check, without trusting us. Seal signs what Discover and Migrate produce, so an auditor, a regulator or a tender committee can verify it on their own machine.

Attest

19 of 19 shipped
  • Every CBOM signed with ML-DSA-65 (FIPS 204), in CycloneDX 1.7
  • Verifiable offline against the signing key's published fingerprint (for kavachq.in, our trust anchor)
  • Signed QBOM, HBOM and AIBOM
  • Signed readiness certificate and vendor scorecard
  • A migration evidence record for each change
  • Tamper-evident audit trail

Monitor

Shipped
  • Scheduled re-scans of the same targets
  • Drift, policy and certificate-expiry alerts
  • Policy-as-code; KPI trends
  • SIEM export and a board paper

KavachQ Gateway

Protect it.

Post-quantum TLS in front of an application you cannot change. Gateway is a proxy you run in your own network. It protects traffic now, while Migrate works through the systems that can be changed.

  • Hybrid key exchange (X25519MLKEM768) first, with classical fallback so no client is cut off
  • The application is not touched; your certificates and keys stay on your host
  • Checked from outside by KavachQ, with a signed record of each check

Scope today: HTTPS applications behind a public endpoint. It protects the key exchange; the certificate stays classical.

Kavach Copilot

In the console: ask the regulation or explain a finding. Answers come from the verbatim text of Indian regulators (RBI, SEBI, CERT-In, DST/NQM, IRDAI, TEC), and each claim is checked before it is shown.

Counts are capabilities in KavachQ's capability register (30 October 2026); planned items are not built yet — two collection methods, and an Envoy change generator. The free scan runs part of KavachQ Discover on your public TLS, instantly. The rest runs in an engagement, in your environment.

Packaged solutions

Two ways in, built from the same products

One finding, start to proof

Follow one weak endpoint all the way to evidence

Discover, Migrate and Seal are one chain. Step through a single finding, from the endpoint Discover sees to the record Seal produces once the change is made.

Discover · Collect

nginx · payments-api

A live TLS probe finds the endpoint and records what it negotiates. Discovery only reads; nothing on the server changes.

Found by
Live TLS probe
Exposure
Internet-facing
Recorded in
The CBOM, in CycloneDX 1.7
Select any stage
Illustrative example · asset names are fictionalMigrate changes TLS terminators only: nginx, HAProxy, Apache, ACME
Where KavachQ sits

You approve every change

Everything else reads and advises. Only Change, inside KavachQ Migrate, changes your systems’ cryptography — and only after a named person on your side signs off.

YOUR ENVIRONMENT

You stay in control

  • Your cryptographic estate and production keys
  • A named approver signs off every change
  • Deploy KavachQ in-VPC, on-prem, or air-gapped
  • Your inventory stays inside your boundary
KAVACHQ

Reads, advises — and changes only what you approve

  • Collect, Assess, Roadmap, Attest and Monitor never change your systems’ cryptography; Roadmap writes only tickets and CMDB records, when you choose to push
  • Migrate prepares a change pack for your team to apply — or, once approved, applies it over SSH with a tested rollback
  • Migrate changes TLS terminators only: nginx, HAProxy, Apache, ACME
  • Every change gets a migration evidence record

Cloud, Kubernetes, HSM and similar sources are parsed from read-only exports you provide — KavachQ holds no cloud credentials.

How KavachQ is deployed Inside your environment (your VPC, data centre or an air-gapped network), KavachQ runs as self-hosted Docker. Inputs: live TLS and SSH probes, an in-network collector bundle, code, configuration and keystores, read-only exports from cloud, Kubernetes, HSM and VPN, and other tools' CBOMs and SBOMs. Outputs: signed CBOM, QBOM, HBOM and AIBOM; tickets to Jira or ServiceNow; SIEM export files; board paper and report; and approved changes to TLS terminators after a named approver signs off. Outside: auditors and regulators verify the signed evidence offline against the signing key's published fingerprint. YOUR ENVIRONMENT · VPC · DATA CENTRE · AIR-GAPPED What it reads Live TLS and SSH probes In-network collector bundle Code, config, keystores Read-only exportscloud · Kubernetes · HSM · VPN Other tools' BOMsCBOM · SBOM imports KavachQ self-hosted Docker Discover Migrate Seal What it produces Signed BOMsCBOM · QBOM · HBOM · AIBOM TicketsJira · ServiceNow SIEM export filesSplunk HEC · ArcSight CEF Board paper and reportPDF Changes you approveTLS terminators only Auditor or regulator verifies the signature offline, against the published key fingerprint OUTSIDE YOUR BOUNDARY
Nothing in your estate has to leave your boundary. Signed evidence travels only when you choose to share it, and it verifies without contacting us.
What you walk away with

Concrete artifacts your board and auditor accept

Not a dashboard you have to live in — portable deliverables you own.

01 · Inventory

A cryptographic inventory (CBOM)

Every certificate, algorithm, and key parameter we can see — a signed CycloneDX 1.7 CBOM your auditors can re-open.

02 · Risk

A ranked quantum-risk register

A T1–T4 tier per asset — algorithm strength, exposure, criticality, cert expiry, and harvest-now risk — and a 0–100 PQC-Ready score for each scan.

03 · Plan

A phased migration plan

A sequenced, impact-aware move to ML-KEM / ML-DSA / SLH-DSA your team can calendar — hybrid by default.

04 · Evidence

A board-ready report

A board PDF + signed CBOM — every finding tagged to your regulator's milestones (in depth today for DST/NQM, RBI, SEBI, CERT-In and IRDAI).

kavachq · board-pack.pdf
BOARD PACK · DST / NQMCBOM ✓ signed
T1 · Critical12
T2 · High34
T3 · Medium88
T4 · Low210
payments-api · RSA-2048T1
core-banking · 3DEST1
vpn-gw · ECDH-P256T2
archive · AES-256T4
TIERED T1–T4 · HNDL-WEIGHTED

Illustrative output — not real customer data.

Inside the console

A tour of the working console

Four real screens, captured on a demo tenant. Pick a view, then select a numbered marker to see what each part of the screen does. The numbers are illustrative, and real client estates never leave your environment.

kavachq console · cryptographic inventory
KavachQ console — cryptographic inventory dashboard: high-risk crypto objects, PQC-ready share, total assets, regulatory exposure, top issues, key types and algorithm families.
  1. 1PQC readiness at a glance

    The share of high-risk crypto objects and of algorithms that are already PQC-ready, across every scan in the tenant.

  2. 2Estate counters

    Total assets, critical findings, quantum-vulnerable assets and harvest-now-decrypt-later exposure, deduplicated across all scans.

  3. 3Regulatory exposure

    The Indian frameworks these findings touch, such as CERT-In, DPDP, DST/NQM and RBI.

  4. 4Top issues, ranked

    Broken algorithms, data exposed to harvest-now-decrypt-later, expired or weakly signed certificates and keys Shor's algorithm breaks, each with a count.

  5. 5Key types

    The key algorithms and sizes in use, from RSA-2048 and EC-256 to the RSA-1024 keys that need replacing first.

  6. 6Algorithm families

    The algorithms and protocols found, from RSA and ECDSA to TLS 1.2, TLS 1.3, AES-256-GCM and Ed25519, ranked by how often each appears.

Captured from the working KavachQ console on a demo tenant · illustrative data · client identities blurred or omitted.

Mapped to the frameworks you report to

Pick a framework. See what you get.

Each framework below lists what KavachQ produces for it and which part of the product produces it. We map evidence to frameworks; we don't certify compliance or replace your auditor.

DST / National Quantum Mission

India · advisory roadmap

India's post-quantum migration roadmap sets milestones by type of organisation. KavachQ places you on it and plans to its dates.

What KavachQ producesDetailFrom
Your DST personaWhere your organisation sits on the DST/NQM roadmapDiscover · Assess
DST-aligned risk tiersA T1–T4 tier per asset and a 0–100 PQC-Ready score per scanDiscover · Assess
A dated migration planP0/P1/P2 work against DST/NQM deadlines, harmonised with global onesMigrate · Roadmap
Signed CBOMCycloneDX 1.7, signed with ML-DSA-65, verifiable offlineSeal · Attest
Board paperReadiness score, cost to migrate and recommended resolutions on one printable pageSeal

Read more: India's migration roadmap

Continuous, not a one-off

Your CBOM should never be last quarter's CBOM

A certificate is reissued, a server is rebuilt, a protocol setting creeps back. Monitor re-scans the same targets on a schedule and tells you what changed, and KavachQ flags when a clause in its regulatory corpus has changed since your baseline.

kavachq · monitor · eventssimulated example
  1. RE-SCAN

    Scheduled re-scan of 412 targets finished · PQC-Ready score 61 → 64

  2. CERT

    *.corp-gw certificate expires in 21 days · alert raised

  3. DRIFT

    api-gw offers TLS 1.0 again since the last scan

  4. REG

    A clause in the regulatory corpus changed since your baseline · alert raised

  5. POLICY

    payments-batch: an RSA-1024 key breaks the baseline policy

  6. SIEM

    14 findings exported in Splunk HEC format

PQC-Ready score · 12 weeksillustrative
64▲ 26 pts since week 1

Readiness over time. Weeks with no scan are shown as gaps, not filled in.

no scan wk 1wk 12
Drift · 7 days9
Certs < 30 days5
Policy breaks23

Illustrative events and figures. Monitor runs as a scheduled or long-running job in your environment; alerts go to a webhook, and findings and alerts can be exported in Splunk HEC or ArcSight CEF format for your SIEM.

How an engagement starts

Start small, prove value, then scale

A low-commitment path — see it work before you widen the scope.

1

Free public scan

Run it on any public domain today. See Discover and Assess on your public TLS in seconds — no sign-in, nothing stored.

NOW · SELF-SERVE
2

Scoped assessment

A scoped engagement on a slice of your estate — supply your certs / CBOM and get a real signed CBOM, a ranked risk register, and a first plan.

SCOPED ENGAGEMENT
3

Deploy in your environment

Run KavachQ where your regulated data lives — in-VPC, on-prem, or air-gapped self-hosted Docker — with no key custody.

IN YOUR VPC
Fits your workflow

Hands off to the tools you already run

KavachQ produces portable artifacts, so the plan lands where your team already works.

Shipping today

Tickets where your team works

The phased roadmap exports as a Jira-ready CSV, or goes straight into Jira and ServiceNow — dry-run by default. Ticket status flows back from Jira, and cryptographic assets can go into the ServiceNow CMDB.

Shipping today

Evidence your other tools read

Findings export to Splunk (HEC) and ArcSight (CEF). The CBOM is signed CycloneDX 1.7; the SBOM is available in CycloneDX or SPDX 2.3; the risk graph is JSON.

Cloud, HSM and similar sources are read from exports you provide; there are no live connectors into your cloud accounts.

Understand it first

We'd rather you learn than be sold to

Free, open material on the quantum threat and India's response — the understanding our team works from.

What you can verify today

Proof you can check yourself

Free public scan

Run it on any domain. The product works in front of you, before any sales call.

Signed CycloneDX 1.7

A standard, machine-readable CBOM — reproducible, portable, no lock-in.

Air-gap-ready

Self-hosted Docker (incl. air-gapped) keeps sensitive estates inside your boundary.

Vendor-neutral

We summarise official DST and NIST sources plainly; no pay-for-placement.

Get started

See your exposure in seconds

Run a free scan, then bring KavachQ to your whole estate — discovery, scoring, planning, and proof, for the regulator you answer to.